The brief
Clinicians coordinate real clinical work on tools built for weekend plans. Theatre lists change by the hour and the coordination happens on consumer WhatsApp, from personal mobiles, or in email threads nobody governs.
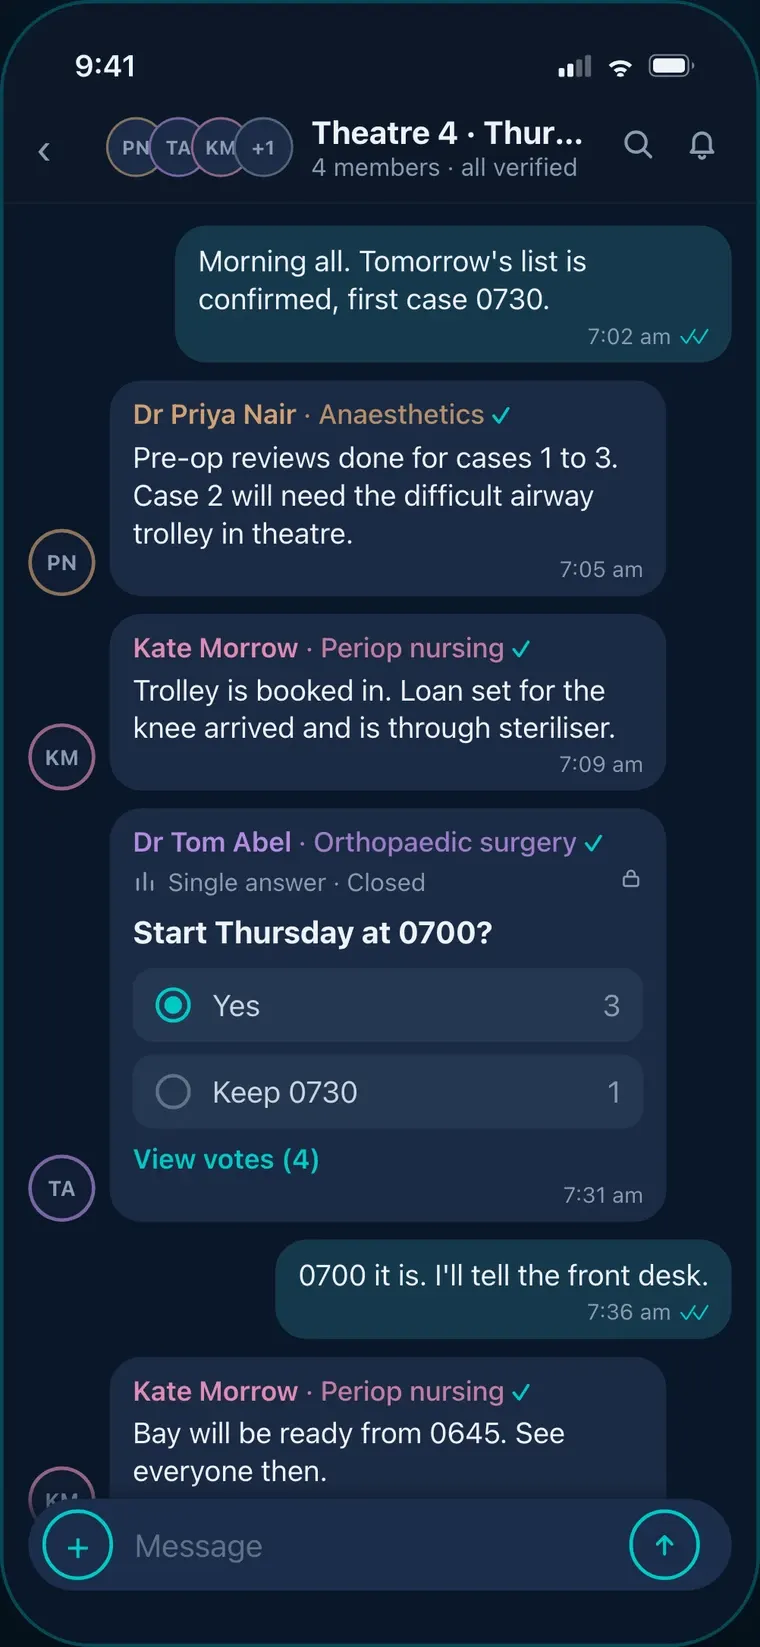
Every one of those has the same three holes. No confirmation the right clinician actually got it. No verified identity behind the name on the screen. And no record, so when something goes wrong months later, reconstructing who said what is guesswork.
We built the app itself, for iOS and Android. The marketing site at synapsechat.app is not ours.
What the app had to do
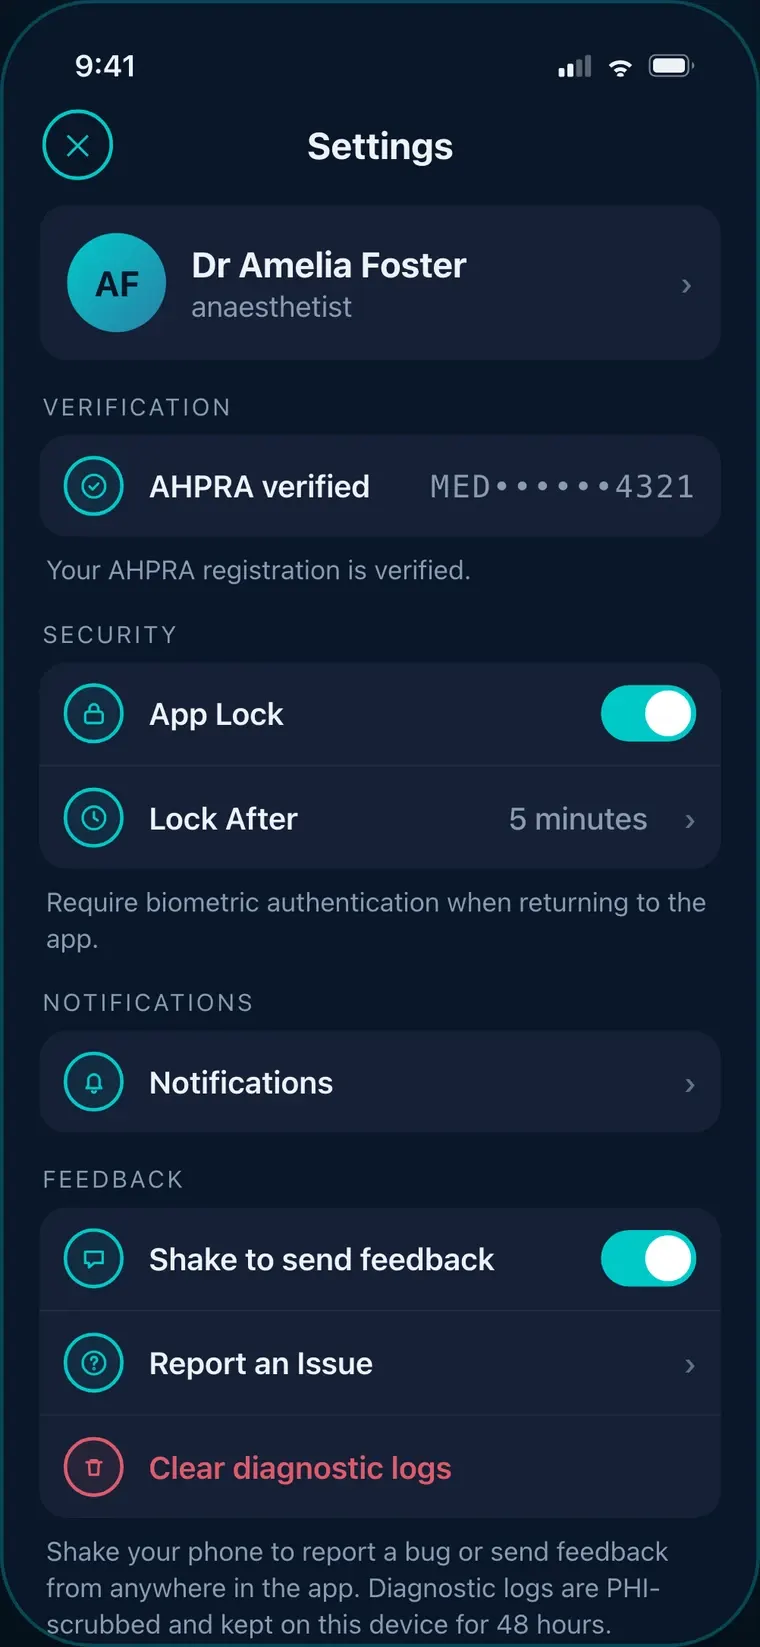
Prove who everyone is. Every account is reviewed by a person before access is granted, including a check that the applicant’s AHPRA registration is current. None of it is automated, because the value of the whole network collapses the first time someone gets in who should not have. The app has to carry that verified state into every screen: who you are talking to, and what they are registered to do.
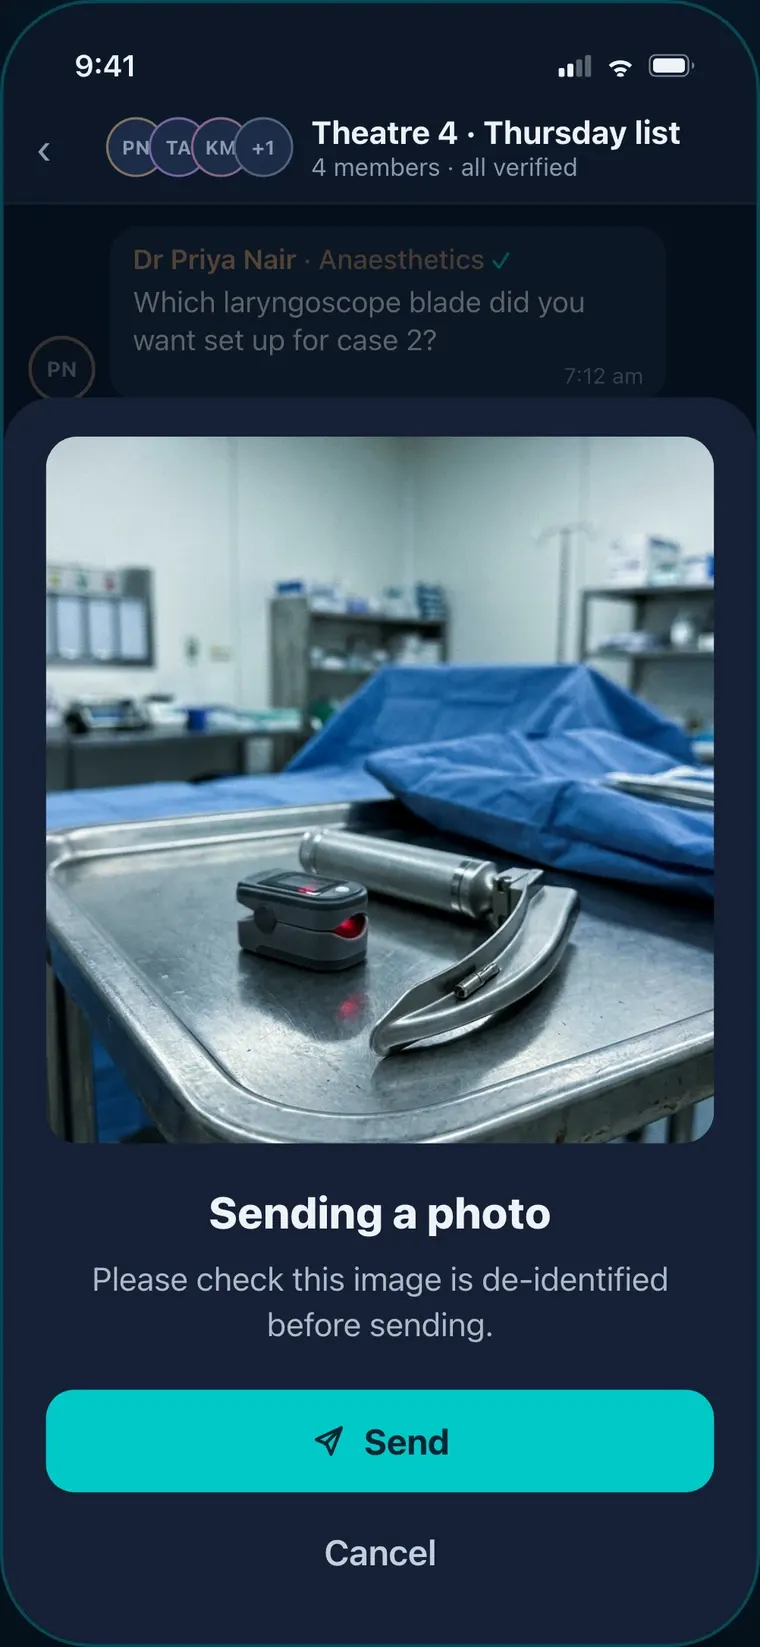
Behave like a clinical tool, not a chat app. Images get a de-identification check before they send. Photos are captured inside the app and sandboxed, so a clinical photo never lands in the phone’s camera roll next to family pictures. That is a build problem rather than a policy one: it is the difference between using the system camera and writing your own.
Keep the data in the country. Australian-hosted, not routinely transferred overseas, built to align with the Australian Privacy Principles under the Privacy Act 1988.
Shipping it repeatedly
A phone app is not a website. You cannot fix a mistake by pushing to main, and two app stores have to agree to let you publish at all, so the work that matters sits in the release pipeline rather than the screens.
Changes move through separate development, testing and production environments, each with its own infrastructure and database migrations, and every release is built the same way whether it is a typo fix or a rewrite. It is on the App Store and Google Play now, with signups still closed behind that manual review.